 Victor Arias
An IT audit for an SMB costs $500-4,000 per project depending on scope, and $4,000-12,000 when there are multiple sites or compliance requirements (ISO 27001, GDPR, PCI-DSS). Hourly rates run $60-120/h and an annual continuous audit plan starts at $300/month. The price depends on the number of systems, the access to be granted and the regulatory framework.
"How much does an IT audit cost?" is the question companies ask us when they've spent months not knowing what they actually have: how many servers, who has access to what, whether email is properly protected or whether the backups are really running. The short answer, in 2026, ranges from $500 to $12,000 depending on scope, but the real price has to be read against what the audit prevents.
In this article I give you realistic market ranges by contracting model (project, hourly and annual plan), explain the four factors that move the price, what a serious report includes and how to compare quotes without ending up with a generic checklist.
How much an IT audit costs in 2026
Indicative ranges for an SMB or mid-sized company, in dollars and excluding taxes:
By project (fixed scope)
- Basic: $500-1,500. Up to 10 systems: inventory, access review, backups and a report with prioritized findings.
- Standard: $1,500-4,000. Network, servers, cloud, email and basic security, with configuration testing and team interviews.
- Complex: $4,000-12,000 or more. Multiple sites, cloud environments, compliance requirements (ISO 27001, GDPR, PCI-DSS) and third-party attestation.
By the hour
- Experienced auditor: $60-120/h in Latin America; $120-250/h in the US and Europe.
- Compliance or cloud specialist: $120-220/h depending on the framework.
Hourly billing only makes sense when the scope is very loosely defined; once you know which systems you want reviewed, a fixed project price is more predictable and removes the temptation to stretch the review.
Annual continuous audit plan
- Quarterly reviews: $300-1,200/month with follow-up reporting and remediation verification.
- With monitoring: $800-2,500/month if continuous configuration monitoring and alerting are included.
To see how an audit fits into maintaining your infrastructure, read our annual infrastructure review guide.
What moves the price: the four real factors
Two companies in the same sector can pay five times more for the same audit. These are the variables that actually move the quote:
The number of systems and the access that must be granted
Every server, application, admin account and device adds review time. And it isn't just counting: granting read-only access, documenting configurations and interviewing whoever maintains each system are hours someone has to bill.
The compliance scope
An audit to tidy up the house is not the same as one that must produce evidence for a certification body. If the goal is ISO 27001, GDPR or PCI-DSS, the work multiplies (policies, records, tests and traceable findings) and so does the price.
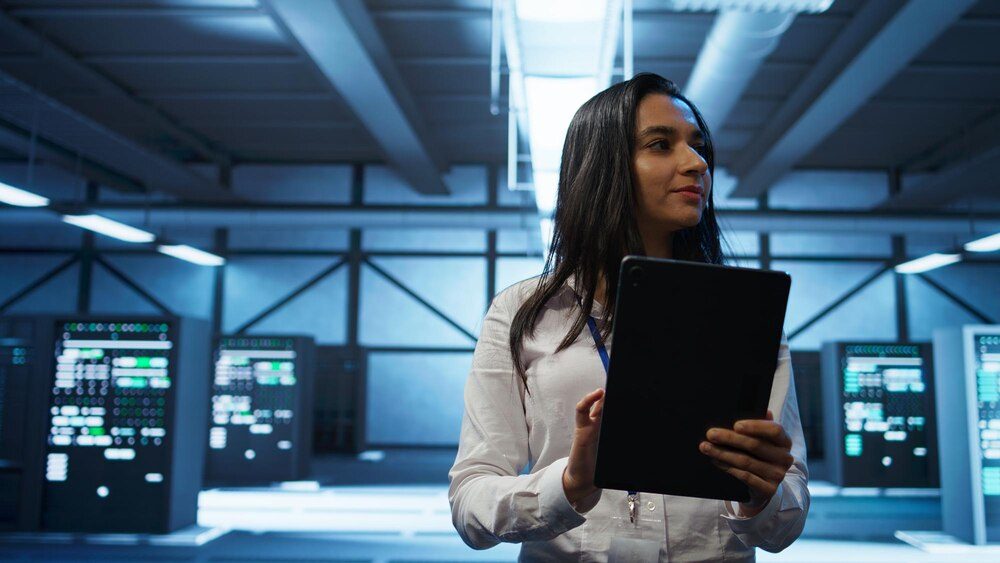
 The audit starts with access, documentation and interviews: that's real time, and it's why the price varies.
What an IT audit includes (and what it doesn't)
Before comparing figures, compare deliverables. A serious audit service includes at least:
- Real inventory of systems, devices, licenses and cloud services.
- Access review: who gets into what, with which privileges, and what should be removed.
- Security: configuration, patching, email, MFA and verified backups.
- Report with prioritized findings, each with its impact, its risk and the steps to fix it.
- Remediation plan and, if contracted, verification that it was applied.
What it does not include: fixing the problems found (that's a separate project), rolling out certifications and, in many audits, the licenses for the scanning tools. Ask for it in writing in the quote.
How to compare audit quotes
Price alone says nothing if each proposal has a different scope. These five steps turn the comparison into something real:
- Ask every proposal for the same scope in writing: systems, sites and included hours.
- Require the report format: findings with severity, remediation and dates.
- Ask who performs the audit: internal auditor, consultancy or freelancer? Experience changes both price and outcome.
- Check independence: whoever audits shouldn't also sell the solution they recommend.
- Add the follow-up: fixing without verifying leaves the risk exactly where it was.
A good report prioritizes work instead of overwhelming you with hundreds of items: that's what turns an audit into executable decisions. And if you also want someone to execute what's found, our IT audit service ends with the remediation plan and its verification.
 A good report prioritizes findings by risk instead of overwhelming you with hundreds of checks.
Common mistakes when hiring an IT audit
- Hiring the cheapest audit and ending up with a generic list nobody executes.
- Auditing without read-only access: the auditor improvises and the report stays incomplete.
- Measuring only compliance and forgetting operations (performance, costs and licenses).
- Not reserving time from your own team: interviews and documentation also cost hours.
- Filing the report with no remediation plan and no verification date.
And one more worth remembering: an audit that finds 200 findings and prioritizes nothing. Volume isn't quality: a report with 8 well-evidenced findings that get fixed in a quarter beats a 200-item PDF that nobody opens again.
If the IT support budget is also on the table, compare it with our guide on how much IT support costs: audit and support are different budgets and shouldn't overlap.
Conclusion: the audit pays for itself with what it finds
A well-run IT audit usually finds, on the first pass, leftover access, unverified backups, unused licenses and outdated configurations: findings that cost money every month they stay unfixed. At that magnitude, a few hundred dollars for an audit is rarely an expense.
At TakeYourDesign we run IT audits for SMBs and mid-sized companies, with prioritized reports and remediation verification. Tell us what you want reviewed and we'll send a fixed-scope quote within 24 hours; if you'd rather start with prevention, check our cybersecurity service too.
Frequently asked questions
How much does an IT audit cost for an SMB?
$500-4,000 per project: basic from $500 and standard between $1,500 and $4,000. Get a fixed-scope quote.
How much does an IT audit for ISO 27001 certification cost?
From $4,000, since it requires evidence and traceability for every finding. See IT audit.
How often should a company audit its systems?
At least once a year; if you handle sensitive data or must comply with regulations, quarterly verified reviews.
What's the difference between an IT audit and a penetration test?
The audit reviews configuration, access and processes; the pentest exploits vulnerabilities. Cybersecurity covers both.
Does the audit price include fixing the problems found?
No: the report prioritizes them and quotes remediation as a separate project. At TakeYourDesign we also execute and verify it.
How do I request an IT audit?
Tell us which systems you want reviewed and we'll send scope and price within 24 hours.