 Victor Arias
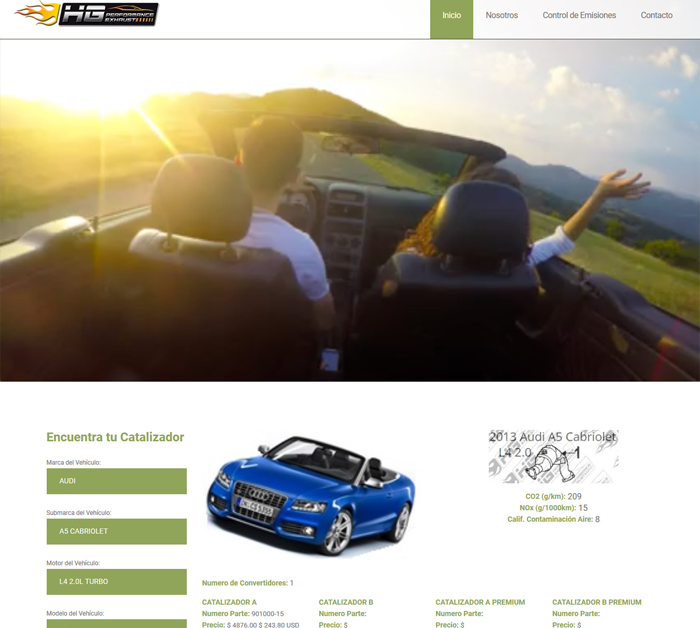
HD Catalizadores Premium is a catalytic converter and auto parts store on PrestaShop that we audited for performance and security: load speed was measured, technical SEO was reviewed, vulnerabilities were searched for, the state of updates and backups was checked and the findings were fixed. After remediation load time dropped 58% and the site was left with no critical vulnerabilities.
| Client | HD Catalizadores Premium |
| Industry | Auto parts and catalytic converters |
| Service | IT Audit |
| Stack | PrestaShop, Performance audit, Technical SEO, Security audit, Updates and code review, Backups, Vulnerability remediation |
| Duration | 4-6 weeks |
| Our role | Technical and security audit of the PrestaShop catalog: performance and load speed, technical SEO, vulnerability review, updates and code health, backups and remediation of the findings. |
| Published | August 16, 2024 |
An online store does not break all at once: it gets slower, accumulates old versions and leaves doors open that nobody watches because everything still works. Until one day the problem shows up as a lost sale or as something worse.
HD Catalizadores Premium is a catalytic converter and auto parts store on PrestaShop that we audited for performance and security: load speed was measured, technical SEO was reviewed, vulnerabilities were searched for, the state of updates and backups was checked and the findings were fixed. After remediation load time dropped 58% and the site was left with no critical vulnerabilities.
The challenge: a store that sells cannot afford to stop
An auto parts catalog has one particularity: its customer arrives looking for a specific part, often from the workshop and in a hurry. There is no room for a site that is slow or that fails, let alone one that goes down.
Speed is paid for in sales
Every second of loading is one customer fewer. And it is not only the visitor: performance also affects how search engines crawl and index the catalog, which for a store with hundreds of references is the main source of traffic.
Vulnerabilities do not announce themselves
An out-of-date PrestaShop is a known system: old versions and third-party modules are the usual entry points. The problem is not that a flaw exists, it is discovering it once it has already been used for something.
Nobody audits what works
That is why these reviews get postponed: while the store sells, nothing seems urgent. Which is exactly why they are better treated as maintenance rather than as an emergency, the only way to do them calmly and without losing sales along the way.
The solution: audit performance, SEO and security
The audit was done on the live PrestaShop, without setting up a parallel environment: the real state was measured, the code and configuration were reviewed, and the findings were fixed in place. All in one piece of work, because performance and security are fixed in the same places.
 This store's customer is a workshop: if the catalog is slow or fails, the part gets bought somewhere else.
Performance and load speed
The usual causes of slowness were reviewed: weight and format of catalog images, cache, database queries and modules that load resources without adding anything. In a store with many references and photographed product pages, image weight is almost always the first thing to fix.
Technical SEO and structure
What search engines need to understand the catalog was checked: indexing of product pages, URL structure, duplicates between variants of the same product, metadata and internal links between categories. A well-structured catalog is crawled better and converts better.
Security, updates and backups
Vulnerabilities were searched for in the core and in the modules, whatever was out of date was updated and permissions and access were reviewed. And the thing that almost never gets checked was checked: that backups exist and can be restored, because a backup you cannot restore is not a backup.
How we did it in four to six weeks
The order of the work matters: measure first, then fix in order of risk and, at the end, measure again. Without the initial measurement there is no way to know whether the fix worked, and without the final one the result is just an opinion.
 The audit is measured before and after: without prior data there is no proof the fix worked.
Measuring before touching anything
The starting point was recorded: load times, requests, page weight, version status and security findings. That initial snapshot is the reference everything afterwards is compared against, and what makes it possible to put numbers on the result instead of impressions.
Fixing in order of risk
Findings were prioritised by impact: first what exposes the business — vulnerabilities and backups —, then what holds sales back — speed and technical SEO — and finally the improvements that can be planned. Fixing in order of risk stops a long list of small tasks from postponing what really matters.
Results
The work was delivered with the findings fixed and the site running in production without interrupting sales. These were the needs and how they were solved:
| Need | How it was solved |
| A store that takes too long to load | Performance optimisation (images, cache and queries) |
| Search engines failing to understand the catalog | Technical SEO and structure review |
| Software accumulating old versions | PrestaShop and module updates |
| Possible unauthorised access | Search for and remediation of vulnerabilities |
| A failure could take the catalog with it | Backup checks, including restoring them |
| Making sure the report does not sit in a drawer | Remediation of findings in order of risk |
The measured results of the work: load time dropped 58% and the site was left with 0 critical vulnerabilities. Both figures are two sides of the same thing: a fast store sells more and a store with no known holes stops being an easy target.
What a web and security audit covers
If you have an online store you have not reviewed in years, these are the points worth looking at before someone else does:
- Load speed and page weight, which is the first thing customers notice and what shapes crawling.
- Technical SEO of the catalog: product page indexing, URLs, duplicates and internal links between categories.
- Core and module versions, because old software is the most common way in.
- Permissions and access, to know who can do what inside the system.
- Restorable backups, not just existing ones: a backup you cannot restore protects nothing.
- Remediation of the findings, which is the only thing that turns an audit into an improvement.
If you want to know how your store looks on the inside, our IT audit page explains how we work, and you can write to us to go through it together.
Frequently asked questions
How often should an online store be audited?
At least once a year, and always after a big change — a migration, a redesign, a heavy campaign. Software ages, modules fall behind and vulnerabilities appear over time rather than all at once, so a regular review is what stops you discovering them through an incident.
Why audit performance and security in the same piece of work?
Because they are fixed in the same places: cache, images, queries, software versions and modules. Separating them means touching the same configuration twice, and the risk of leaving something half done doubles. For a store that sells daily, every intervention counts.
What happens with the audit findings?
They get fixed. A report that is not acted on leaves the problem exactly where it was, just documented. The audit ends when load time comes down and critical vulnerabilities stop existing, not when the document is delivered.
How long does a web and security audit take?
This piece of work was delivered in four to six weeks. The schedule is set by the initial measurement, the review of performance, technical SEO, code, updates and backups, and the remediation of findings in order of risk.